Decoding Encryption Standards That Govern Secure Transactions in Progressive Jackpot Networks Across Global Platforms
Sam Walter · Aug 29, 2026
Decoding Encryption Standards That Govern Secure Transactions in Progressive Jackpot Networks Across Global Platforms
Progressive jackpot networks link numerous online platforms so that contributions from players worldwide accumulate into shared prize pools and those pools require constant data exchange between operators and financial processors, and encryption protocols protect every transaction from interception while the funds move across borders. Standards bodies such as the National Institute of Standards and Technology publish specifications that define how algorithms like AES-256 operate in these environments, and network operators integrate those algorithms into payment gateways so that card details and withdrawal requests remain unreadable during transmission.
Core Algorithms in Use Today
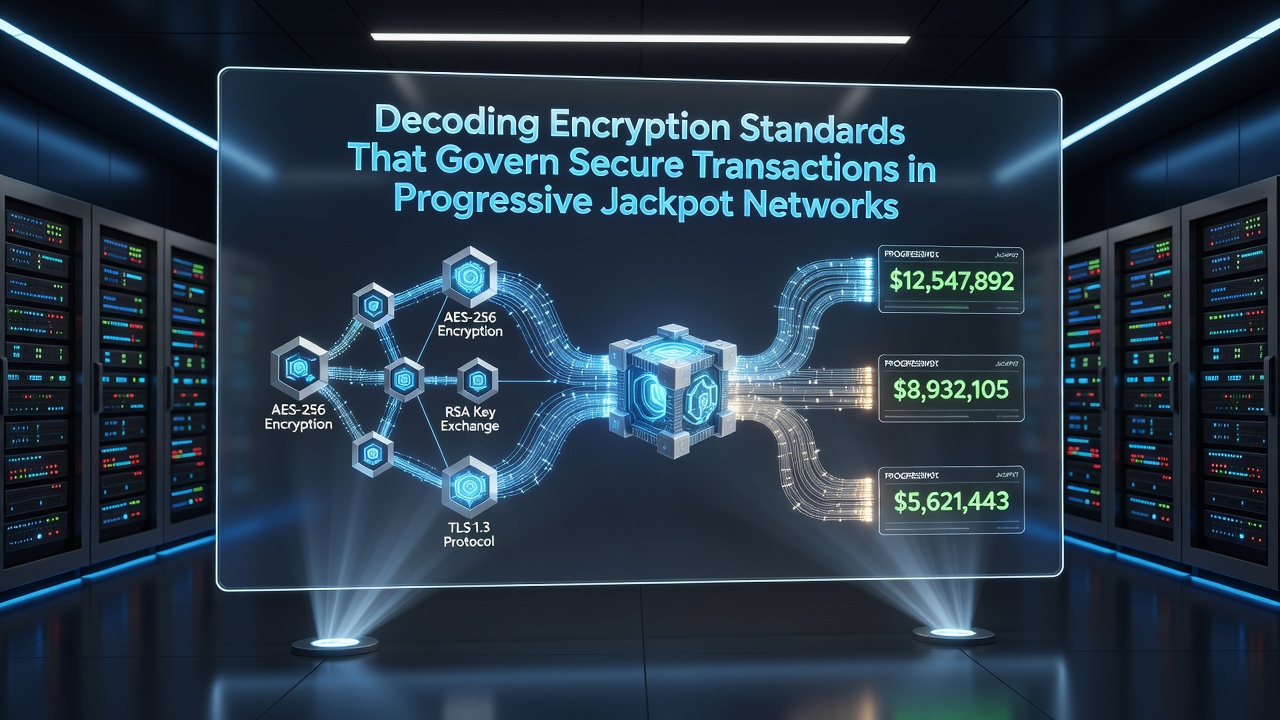
AES operates as a symmetric block cipher that encrypts and decrypts data with the same key, and regulators in North America require its 256-bit variant for all jackpot-related traffic because the algorithm resists known brute-force attacks when implemented correctly. Elliptic-curve cryptography supplements AES by handling key exchange and digital signatures, and developers select curves such as secp256r1 because shorter key lengths deliver equivalent security to larger RSA moduli while reducing computational overhead on high-volume jackpot servers. Researchers at institutions including the University of Waterloo have published analyses showing that properly configured elliptic-curve implementations maintain forward secrecy even if one session key is later compromised.
Transport Layer Protections
TLS 1.3 became the mandatory transport protocol for progressive systems in many jurisdictions after earlier versions were deprecated, and the protocol negotiates cipher suites that combine AES-GCM or ChaCha20-Poly1305 with elliptic-curve Diffie-Hellman so that jackpot contribution messages and payout instructions travel inside authenticated encrypted channels. Certificate authorities issue extended-validation certificates to operators, and automated revocation checks prevent platforms from accepting certificates that have been withdrawn following security incidents. Data in transit therefore stays protected while the same standards apply to API calls that update jackpot meters every few seconds across continents.
Regional Compliance Requirements
European operators follow guidelines issued by ENISA that reference the same AES and TLS specifications yet add requirements for regular penetration testing and key-rotation schedules, and Australian regulators reference similar technical controls through the Interactive Gambling Act framework. In Canada the Alcohol and Gaming Commission of Ontario mandates that progressive networks undergo third-party audits verifying encryption strength before any license renewal, and those audits examine both live transaction logs and stored backup files. South African authorities similarly require proof that jackpot data crossing into neighboring countries uses encryption that meets or exceeds ISO/IEC 18033 standards.
Key Management and Storage Practices
Hardware security modules store the master keys that encrypt jackpot ledgers at rest, and access policies restrict administrative entry to personnel who authenticate through multi-factor procedures, and logs of every key retrieval feed into compliance reports submitted to oversight bodies each quarter. When operators migrate keys during routine rotations the process occurs inside isolated environments so that plaintext values never appear on general-purpose servers. August 2026 marks the deadline by which several European platforms must demonstrate migration to post-quantum key-exchange methods that remain under evaluation by NIST, and early adopters already run hybrid implementations that combine classical and quantum-resistant algorithms during test transactions.
Integration with Payment Rail Security
PCI-DSS requirements intersect with gambling-specific rules because progressive networks process card payments that fund the jackpot pools, and merchants must segment cardholder data behind additional encryption layers that use format-preserving techniques so that the data remains usable for reconciliation yet unreadable outside the payment domain. Tokenization replaces actual account numbers with surrogate values before any information reaches the jackpot engine, and the mapping tables reside inside separate vaults that employ their own AES instances. This layered approach ensures that even if one segment of the network experiences a breach the financial details stay protected.
Monitoring and Incident Response
Continuous monitoring platforms scan encrypted traffic metadata for anomalies without decrypting payloads, and anomaly detection models flag unusual jackpot meter spikes that could indicate manipulation attempts. When alerts trigger, incident response teams isolate affected nodes and rotate session keys within minutes, and post-incident reports submitted to regulators detail the timeline and the cryptographic controls that limited exposure. Observers note that such rapid responses rely on pre-shared key hierarchies that allow segments of the network to continue operating while compromised portions are rebuilt.
Conclusion
Encryption standards that govern progressive jackpot transactions combine established algorithms, transport protocols, and regional compliance frameworks to keep player funds and prize pools secure across global platforms, and ongoing updates such as the 2026 post-quantum transition demonstrate how the field continues to evolve in response to new threats while maintaining interoperability among operators in multiple jurisdictions.